Remote identity verification is checking that a person is who they claim to be without meeting them, and EU anti-money laundering rules accept it for account opening, but not every method counts equally. For compliance teams at banks, fintechs, law and accounting firms, the question is no longer whether remote onboarding is allowed. It is which method the rules treat as the default, and which one you will have to justify. From July 2027 the answer tilts clearly towards electronic identification and qualified trust services, with document-and-selfie checks becoming the fallback.
Key Takeaways
Four methods: a video call with an agent, an unattended document check with a live face capture, an eID means or EU Digital Identity Wallet, and a qualified signature certificate.
The default shifts in 2027: the Anti-Money Laundering Regulation applies from 10 July 2027 and names eID means and qualified trust services as a verification route in its own right.
Document and selfie becomes the exception: AMLA's final draft standard on customer due diligence lets firms use other remote measures only where they can justify why the customer could not use eID or a qualified trust service.
Method
How it works
Main rule today
From July 2027
Video call with an agent
Trained staff check the document and the face live
EBA GL para 42
Alternative; must be justified
Unattended document + face capture
Software reads the document, matches a live face to its photo
EBA GL para 41 (liveness required)
Alternative; must be justified
eID means or EUDI Wallet
Person logs in with a notified national eID or wallet
AMLR Art. 22(6)(b)
Default route
Qualified signature certificate
Identity was proven when the certificate was issued
AMLR Art. 22(6)(b)
Default route
What Is Remote Identity Verification?
Remote identity verification is any process that confirms a person's identity when they are not physically in front of you. It has two parts: collecting identity evidence (an identity document, an eID login, a certificate) and binding that evidence to the person actually present on the other side of the screen. The second part is where remote methods differ, and where fraud happens.
You will also see the term remote identity proofing. In practice the two are used interchangeably. The European standard for trust service providers, ETSI TS 119 461, speaks of identity proofing and sets two levels: Baseline and Extended Level of Identity Proofing. AML law speaks of identification and verification of the customer. No official source draws a sharp line between the two terms, so treat them as the same activity seen from two regulatory angles.
What Are the Methods of Remote Identity Verification?
There are four methods, and EU rules recognise each of them in some form. Article 24(1a) of the eIDAS Regulation as amended by Regulation (EU) 2024/1183 lists the ways a qualified trust service provider may verify a person before issuing a qualified certificate: an EU Digital Identity Wallet or notified eID at assurance level high, an existing qualified signature or seal certificate, physical presence, or other identification methods that give a high level of confidence, confirmed by a conformity assessment body. That last category is where video and unattended remote checks sit.
Video call with an agent. A trained employee sees the person live, inspects the document on camera and follows an interview guide. The EBA Guidelines (para 42) require exactly that training and guide. It is slower and needs staff on shift, but a human catches context that software misses.
Unattended document and face capture. The person photographs their document, the software reads it (often the NFC chip in a passport), and a live capture of the face is compared with the document photo. The EBA Guidelines (para 41) require liveness detection and that the images are taken during the session, plus randomness in the actions asked of the person (para 43) to counter synthetic identities. This is the method most fintech apps use.
eID means or EUDI Wallet. The person logs in with a national electronic identity that the state has notified under eIDAS, or from late 2026 with an EU Digital Identity Wallet. The identity was checked once by the issuer; you rely on that check. Coverage is the weakness: notified eIDs are national, and wallets are only now arriving.
Qualified signature certificate. If the person already holds a qualified certificate, the provider that issued it has verified their identity under eIDAS Art. 24. Signing with it carries that verified identity into your process.
Does Remote Identity Verification Meet AML Requirements for Account Opening?
Yes, remote verification meets EU AML requirements for account opening today, provided the method is reliable and documented. For banks and other financial institutions, the EBA Guidelines on the use of remote customer onboarding solutions (EBA/GL/2022/15) set the bar. If the evidence is poor quality, the process must stop or be redirected to face-to-face verification (para 40). The Guidelines also treat the criteria as met where the solution uses notified eID at substantial or high assurance, or relevant qualified trust services (para 45).
National rules still add detail until 2027. Spain, for example, lets firms skip a copy of the ID document when the client's identity is checked with a qualified electronic signature, under Article 12 of Ley 10/2010. Germany and France have their own lists. Check the rule in each country where you onboard clients. Our guide to KYC in Spain covers all four Spanish routes.
The common thread: whatever method you use, you must be able to show afterwards what was checked, when and by whom. A pass/fail flag from a vendor is not evidence. Keep the record of the check itself.
What Changes Under AMLR in July 2027?
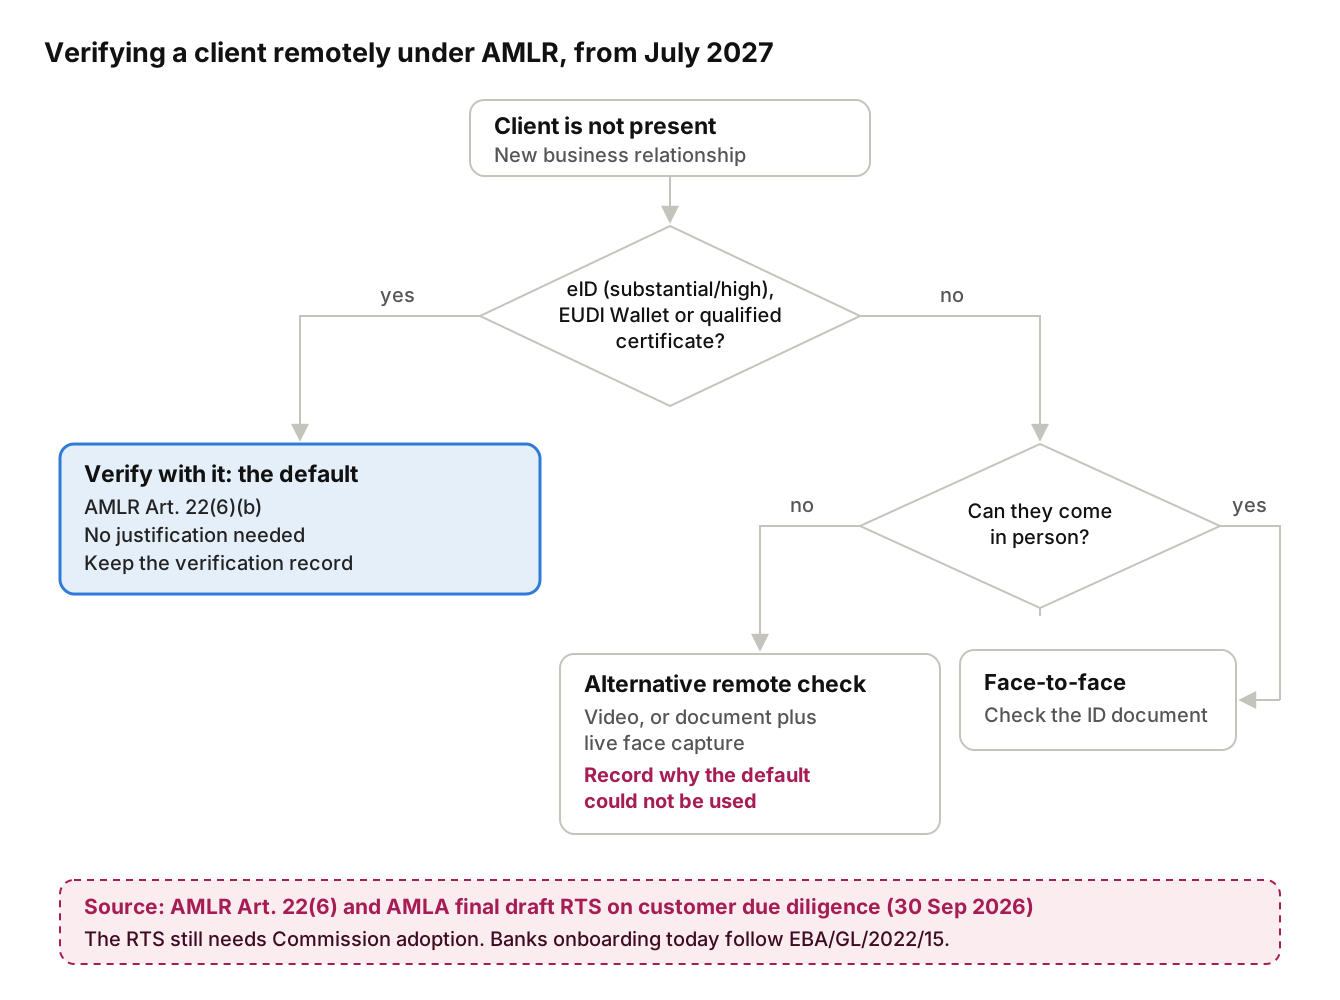
From 10 July 2027, one EU regulation replaces national transpositions of the AML directives, and it states the verification routes directly. Article 22(6) of Regulation (EU) 2024/1624 allows verification by (a) an identity document, passport or equivalent, or (b) "electronic identification means which meet the requirements of Regulation (EU) No 910/2014", at assurance level substantial or high, and "relevant qualified trust services".
The detail comes from AMLA. Its final draft regulatory technical standard on customer due diligence, published on 30 September 2026, says eID means and qualified trust services should be used wherever possible, including EU Digital Identity Wallets. Other remote measures, such as a document check with captured images or video, are an alternative. A firm may use them only where the customer cannot present the document in person and has no eID or qualified trust service, and it must justify why. The standard still goes to the Commission for adoption and applies six months after it enters into force.
Two things follow. Firms that built onboarding around document-and-selfie checks can keep them, but they will need a written reason each time. And the burden of proof flips in favour of eID and qualified certificates. Our AMLR guide and the post on what AMLR requires from small firms before July 2027 cover the rest of the regulation.
How Do You Know a Remote Verification Method Is Reliable?
Ask which standard it is audited against, and who audits it. For qualified trust service providers the answer is fixed by law: Commission Implementing Regulation (EU) 2025/1566 makes ETSI TS 119 461 V2.1.1 the reference standard for verifying identity before issuing qualified certificates, from 19 August 2027. A conformity assessment body audits the provider against it, and the national supervisor decides whether the provider stays on the EU Trusted List.
What that looks like from the inside: ZealiD's own published practice statement describes unattended remote proofing at the Extended Level of Identity Proofing, run as a hybrid of automated checks and human review. The automated face-to-document match returns one of seven confidence levels, and only the highest allows a fully automated decision. Everything below goes to a trained registration officer, whose training covers detecting presentation and injection attacks. Ask any vendor the same questions: what happens to the cases the software is unsure about, and who looks at them? Our post on injection attacks versus liveness checks goes deeper on the attacks.
Where Does Remote Identity Verification Still Fall Short?
Remote verification works best for people with a modern identity document and a smartphone, and worst for everyone else. Three gaps are worth planning for.
Non-residents. eID schemes are national. A client from another country often cannot use your country's eID, and EU Digital Identity Wallets do not yet fill the gap. Document-based methods cover more nationalities but now need justification under the AMLA standard.
Institutions that don't accept what they should. ZealiD's CEO, Tomas Zuoza, described a foreign national who could not log in to the Lithuanian Center of Registers without a Lithuanian personal code, and whose emailed submission was then rejected because a digital channel existed. "It took us 1.5 years and a formal intervention from the European Commission" to get email submissions accepted. A valid remote identity does not guarantee every counterparty will accept it.
Document coverage. Unattended checks only work for documents the system knows. Ask for the list. ZealiD's covers more than 265 identity documents from over 50 nationalities; a provider that cannot give you a number is guessing.
What Should You Look For in a Remote Identity Verification Provider?
Choose on four criteria: which of the four methods it supports, which standard it is audited against and by whom, what happens to uncertain cases, and whether the evidence it keeps would satisfy your supervisor years later. A method that is the default under AMLR (eID, wallets, qualified certificates) saves you the justification the AMLA standard will ask for.
ZealiD is a Qualified Trust Service Provider on the EU Trusted List, supervised by the Swedish Post and Telecom Authority. Its remote identity verification takes about three minutes with no video call, and the verified identity is what its qualified electronic signature is issued on.
FAQ
What is remote identity verification?
Remote identity verification confirms that a person is who they claim to be without meeting them in person. It combines identity evidence, such as a document, an eID login or a qualified certificate, with a check that the person present is the owner of that evidence.
What is remote identity proofing?
Remote identity proofing is the term used in trust service standards such as ETSI TS 119 461 for the same activity. It covers collecting identity evidence remotely and binding it to the person. AML law calls it identification and verification of the customer.
Does remote identity verification meet regulatory requirements for account opening?
Yes. EU banks may onboard remotely under EBA Guidelines EBA/GL/2022/15, in force since 2 October 2023, and from 10 July 2027 the AML Regulation names eID means and qualified trust services as a verification route. Document-and-selfie methods remain allowed but will need justification.
What does AMLR say about remote identification?
Article 22(6) of the AML Regulation allows verification with an identity document or with eID means at assurance level substantial or high and relevant qualified trust services. AMLA's final draft standard of 30 September 2026 makes eID and qualified trust services the default for remote onboarding.
Is a selfie with liveness detection enough for AML?
Today, for EU banks, it can be, if it meets the EBA Guidelines: images taken during the session, liveness detection and a reliable match to the document photo. From 2027, AMLA's standard treats it as an alternative that firms must justify when the customer has no eID or qualified trust service.
How long does remote identity verification take?
It depends on the method. An eID login takes seconds if the person already has one. An unattended document and face check usually takes a few minutes. With ZealiD it takes about three minutes, and 85% of people pass on the first try.
Tomas Zuoza is CEO of ZealiD, a Qualified Trust Service Provider listed on the EU Trusted List, supervised by the Swedish Post and Telecom Agency (PTS) under the eIDAS regulation. He has spent over nine years at ZealiD across business development, operations, and product, leading the company through its 2020 milestone as the first EU trust service provider to issue qualified electronic signatures via fully automated, non-video registration. Before becoming CEO in 2025, he served as Chief Product Officer and COO, building ZealiD's signing infrastructure and expanding its certification portfolio to include qualified time stamps. His expertise spans GDPR, information security, and NIS2 compliance, and he now leads the development of Trust Circle, a verified workspace for professional services firms and their clients.